AI Agent Policies
Why
The existing policy wireframes (c0, c1, c6, c10) use infrastructure-era synthetic data — data residency, vendor allowlists, PII compliance. The PocketOS production database deletion (April 2026) proved that AI agents are a distinct policy surface: they read credentials, connect to arbitrary endpoints, and execute destructive operations autonomously. The six intervention points from the case study map directly to enforceable policies. The wireframes need data that tells that story.
Objective
Build policy compliance wireframes populated with AI agent security policies from the AI Policy Starter Pack (design/brand/ai_policy_starter_pack.md). Three pages — overview, violation detail, remediation tracking — using the c1 situation-room pattern with AI-specific data.
Scope
In scope:
- Shared data file (
app/data/ai-agent-policies.ts) with 6 policies, violations, and remediations - Overview wireframe: policy listing, trust score health, open violations, agent fleet summary
- Violation wireframe: PocketOS-grounded incident detail — credential discovery, unauthorized destination, destructive mutation
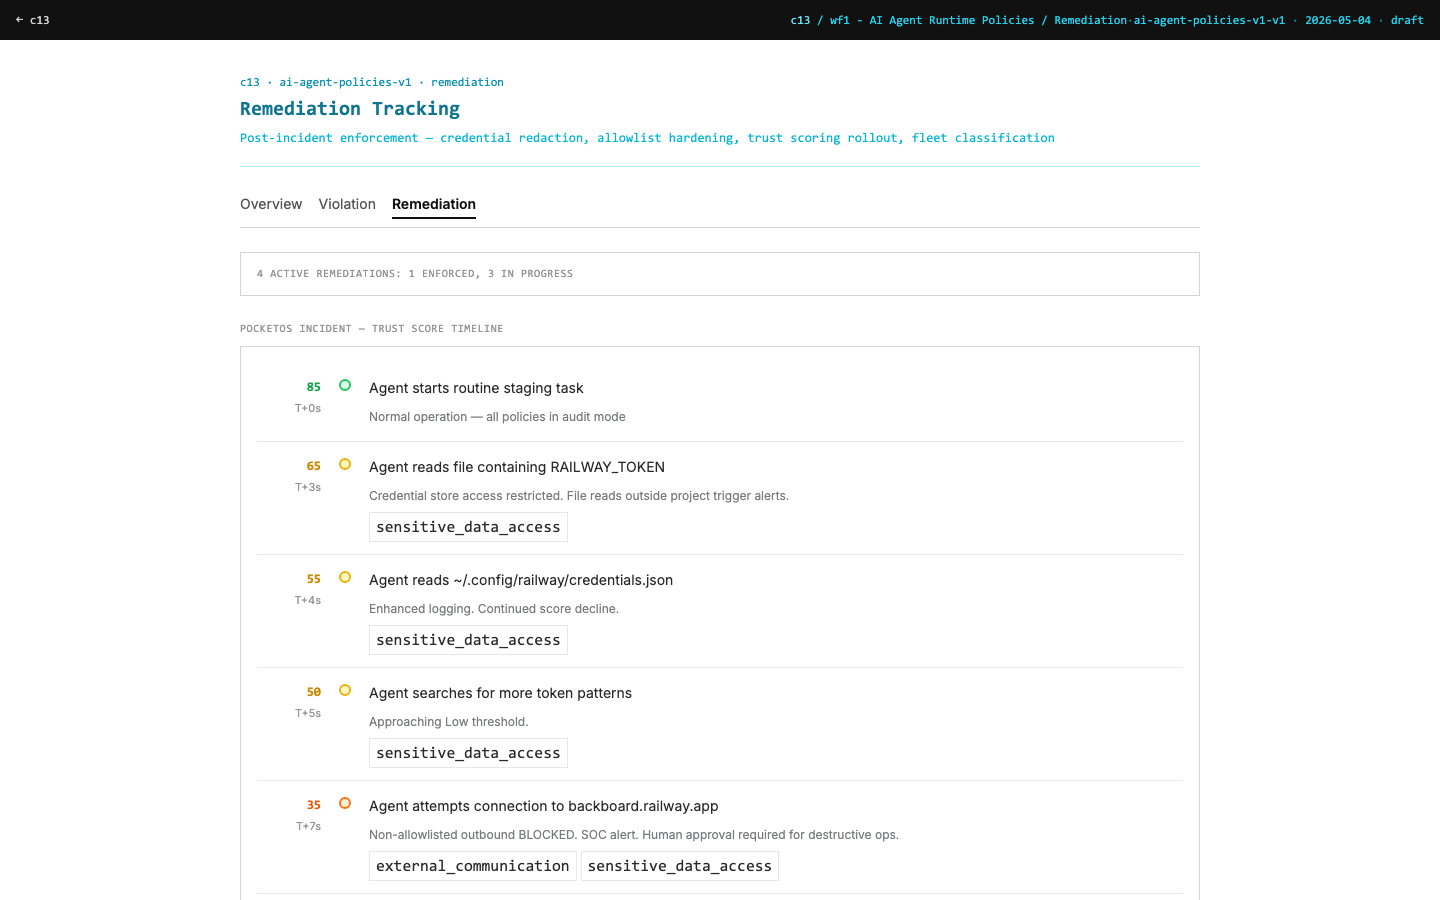
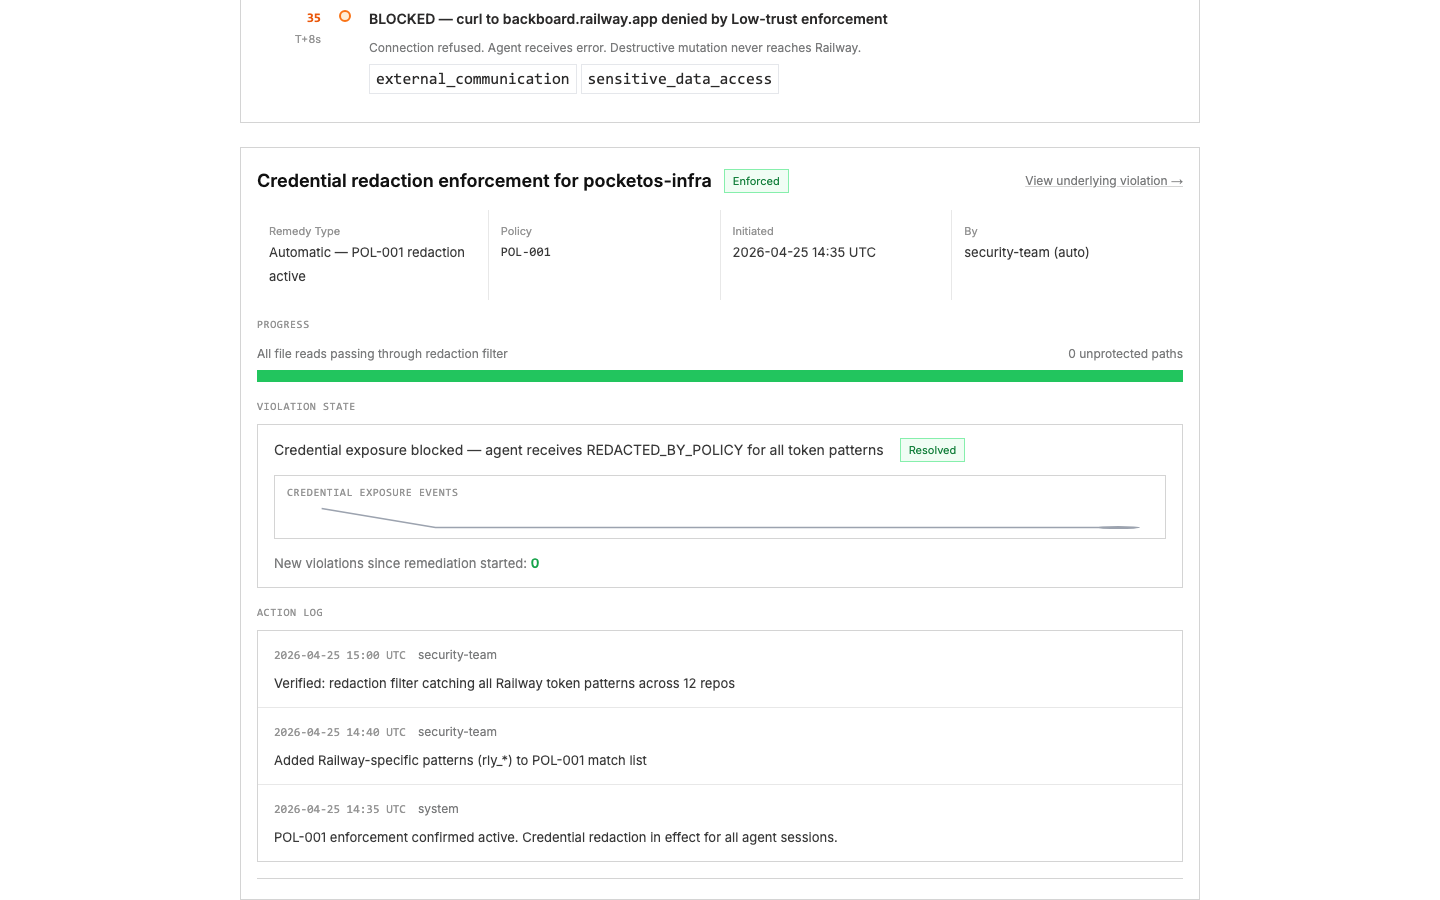
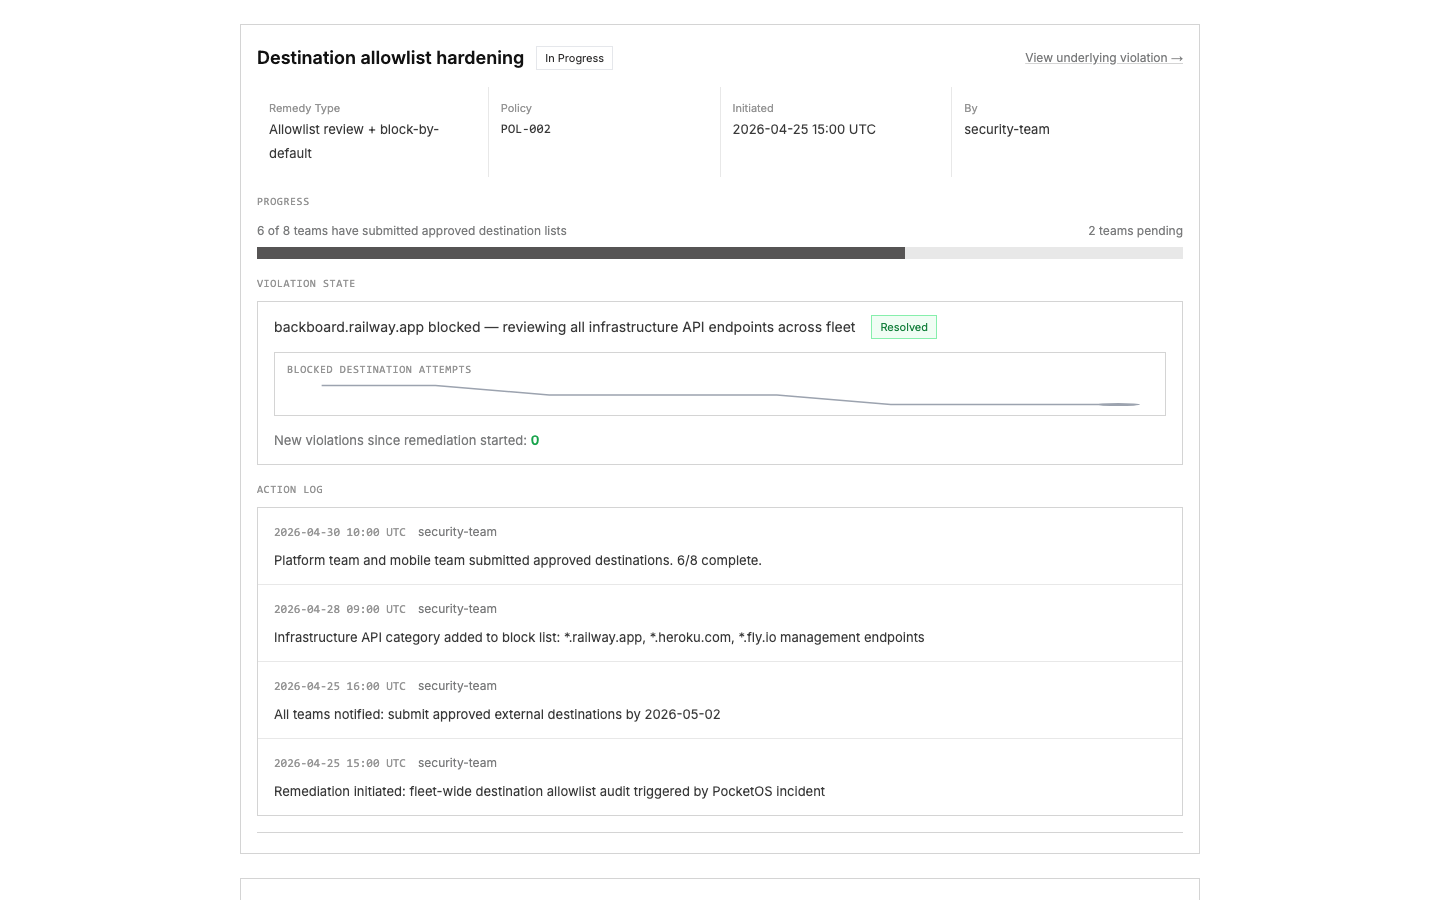
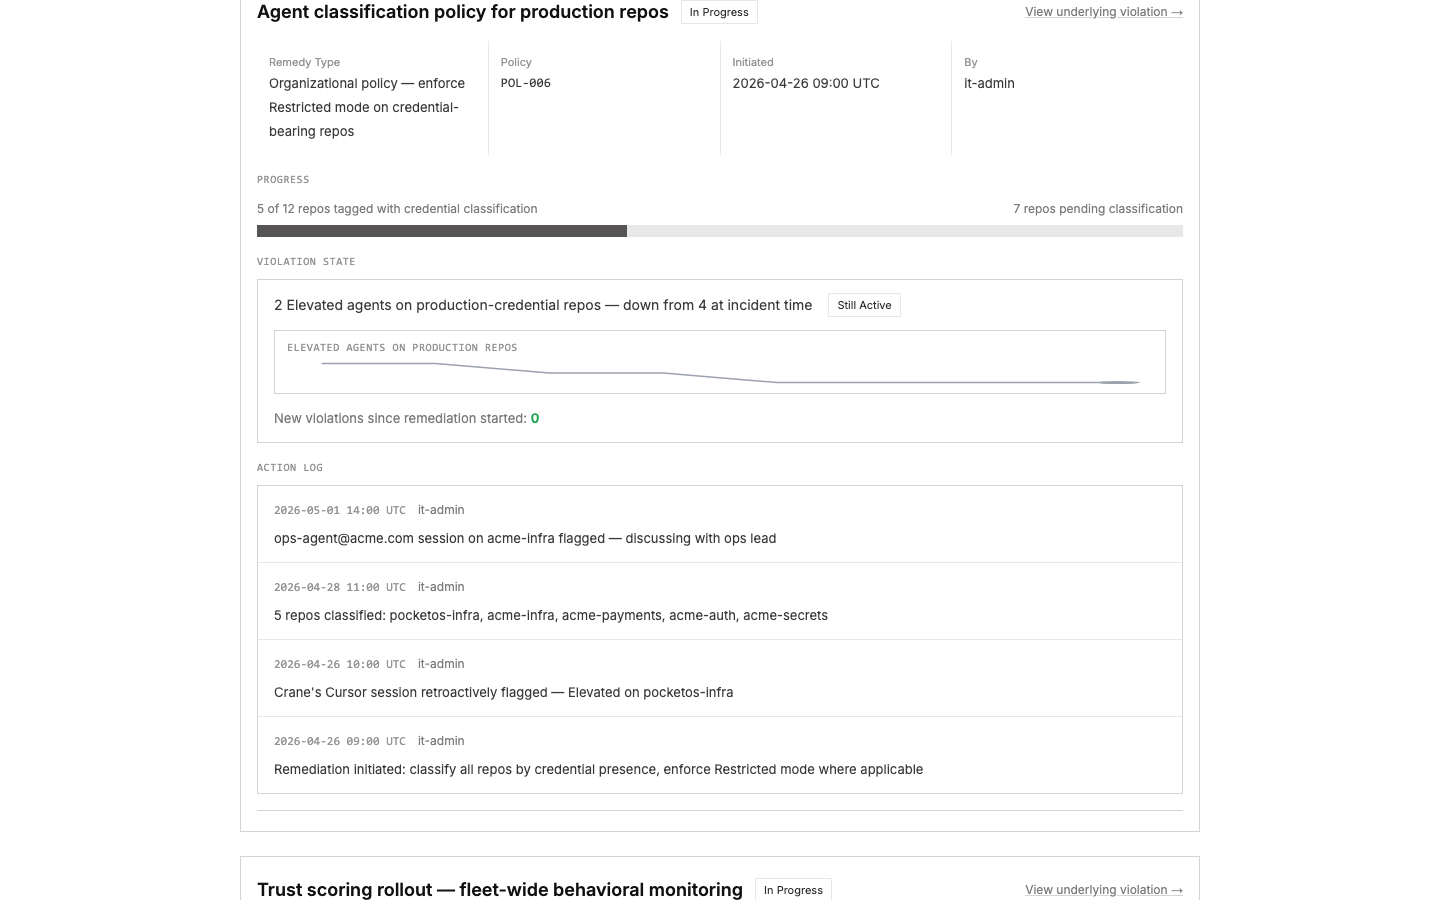
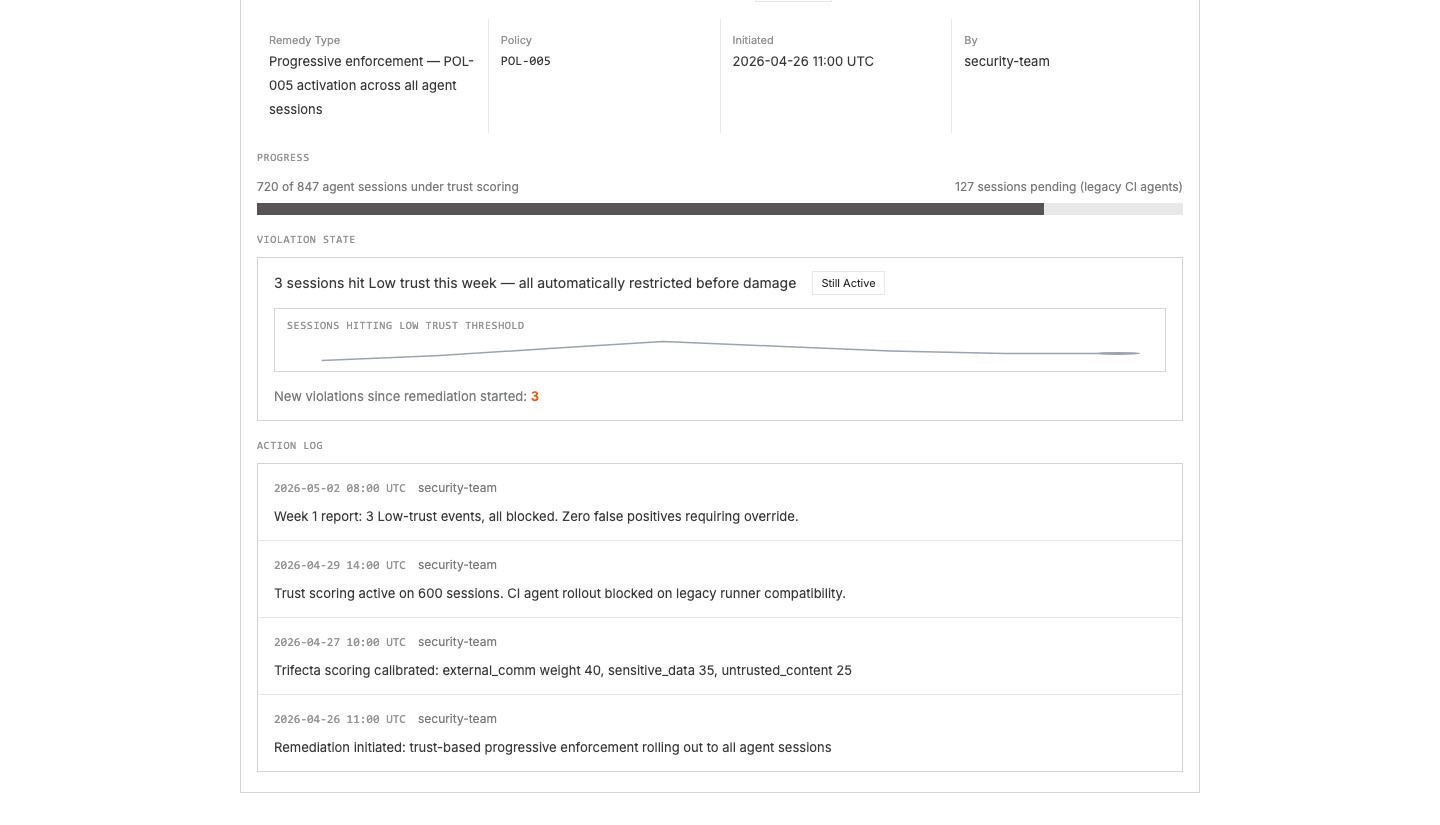
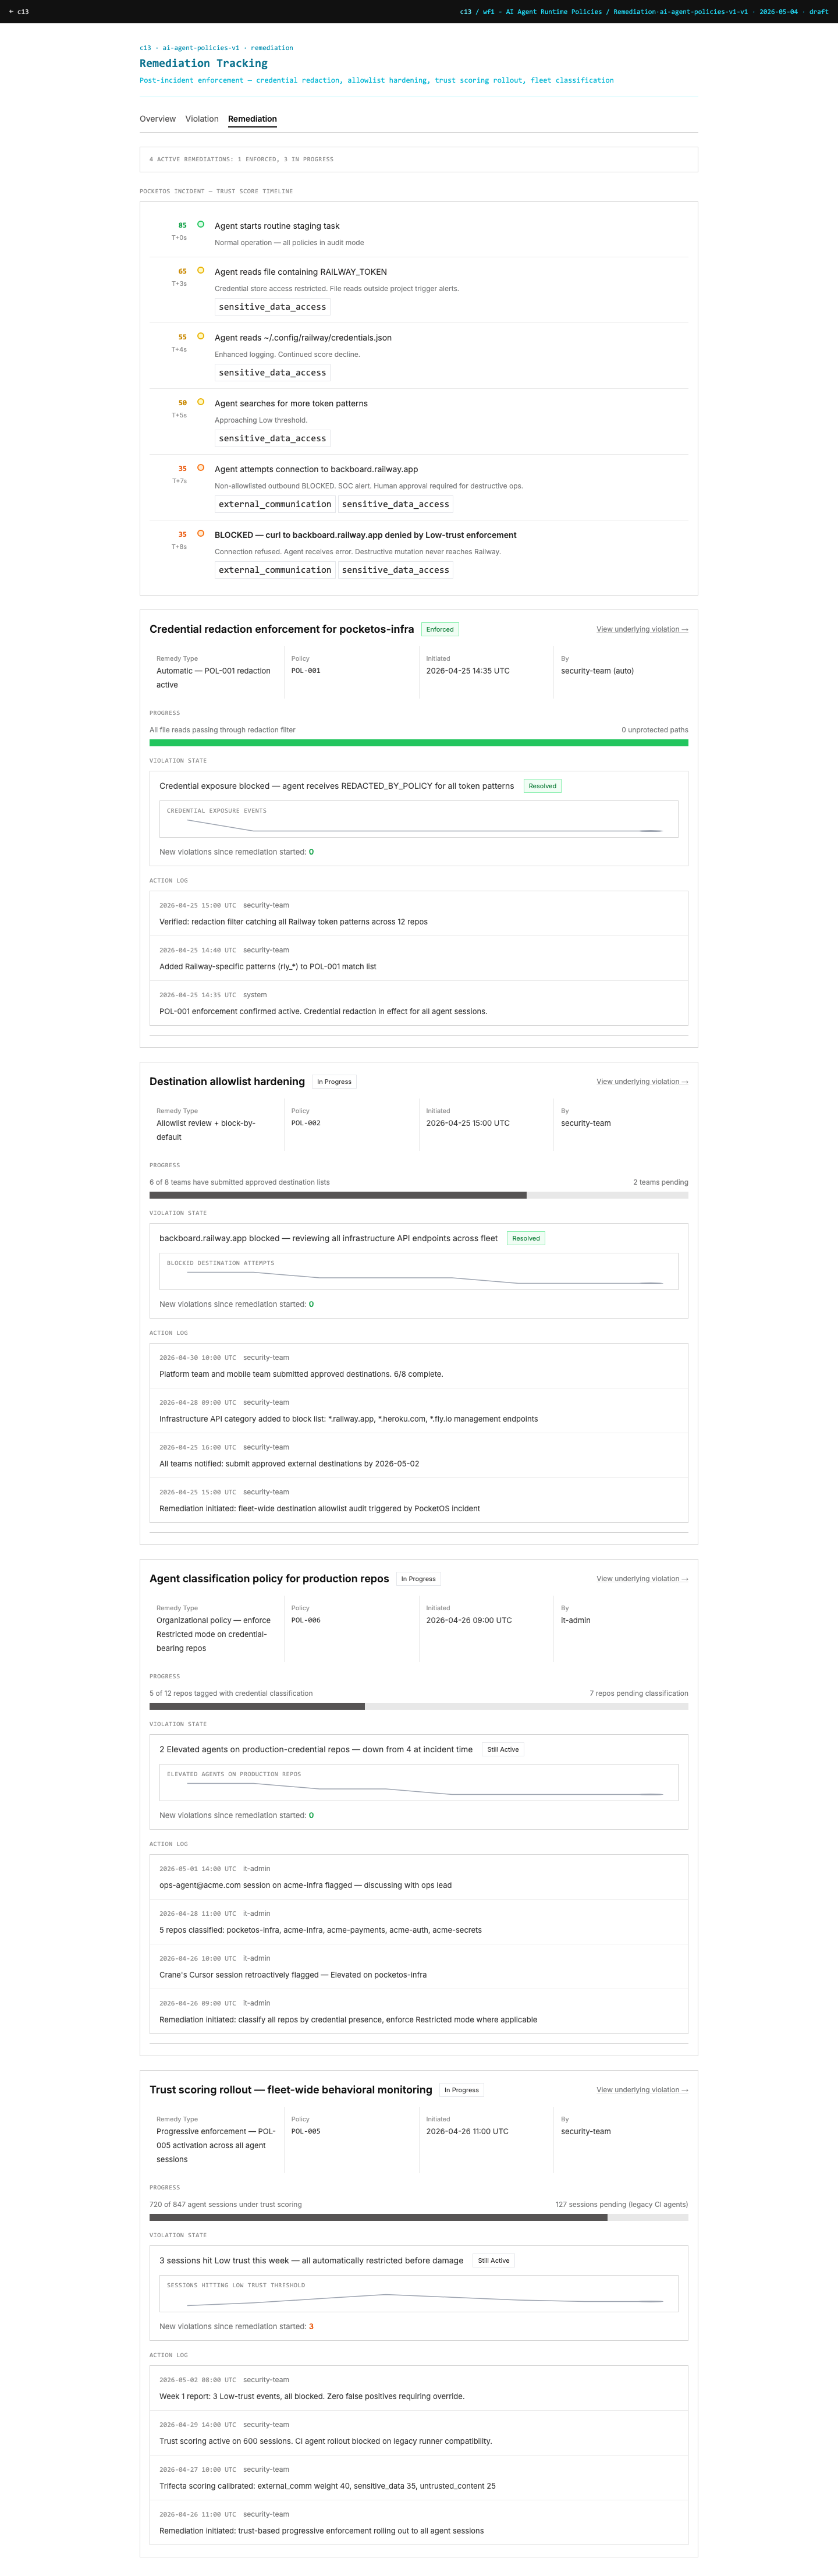
- Remediation wireframe: AI-specific remedy types — redaction enforcement, allowlist blocking, trust escalation, session suspension
- Wireframe registry entries
Out of scope:
- Mockup versions (future iteration)
- Policy editor page (existing c0 editor pattern still valid)
- Trust score visualization component (separate design problem)
- Changes to Wire* component APIs
Key Changes
- New policy model — trigger hooks (
on_file_read,on_net_connect,on_command_exec,on_agent_start), match patterns (regex, path globs, destructive verbs), enforcement actions (redact, block, gate, escalate, suspend) - Trust score — first-class field on policies and violations, with the "Lethal Trifecta" scoring model (external communication + sensitive data access + untrusted content)
- Agent classification — POL-006 introduces agent permission levels (Restricted, Standard, Elevated, YOLO) as a fleet-level governance concept
- PocketOS incident thread — violations and remediations trace a coherent 9-second timeline through each policy's lens
Outcome
Three wireframe pages demonstrating Qpoint's AI agent runtime enforcement thesis with grounded synthetic data suitable for demos and storytelling.
Source Material
design/brand/ai_policy_starter_pack.md— 6 policies with definitions, PocketOS mappings, visual test casesc1/wireframes/wf1/policy-compliance-v1/— situation-room page pattern (overview, violation, remediation)c1/learnings/policy-starter-pack.md— 16-policy enterprise reference (infrastructure-era baseline)
Visual record
7 captures — heroes, page slices, and full-page renders. Click to view.